Your MIM transition window is open today.
Microsoft Identity Manager extended support ends January 9, 2029. Higher education procurement takes two to three years. Start now and you choose on your own terms.
Jan 12, 2021
Mainstream support ended
Jan 9, 2029
Extended support ends
2-3 years
Higher ed procurement cycle
…
…
Until extended support ends
MIM transition
Don't trade one Microsoft-scoped platform for another.
If your campus runs LDAP, SQL, SAP, Oracle, PeopleSoft, and non-Microsoft directories, this matters. MIM and Entra ID Governance are both Microsoft-centric. Neither covers that on-premises and non-Microsoft work in full.
Bravura Identity covers what both leave out. Entra ID remains your cloud and Microsoft foundation, and Bravura Identity governs the systems around it.
You will use Microsoft Entra ID. You will still need Bravura Security for what it does not cover.
One decision, three viewpoints
Built for how campuses actually run.
Your leadership, identity team, and IT managers each need something different from this decision.
Decide on your timeline, not Microsoft's.
Start your evaluation in 2027 and you choose under deadline pressure. Start now and you choose on your own terms.
Begin with Bravura Identity, then extend to Bravura Privilege and Bravura Safe. You modernize identity, privilege, and secrets on one platform and one timeline, not three projects.
Connectors, not custom code.
MIM typically needs custom .NET rules or PowerShell scripting to reach non-Microsoft systems. Bravura Identity gives you a broad out-of-the-box connector library and a standard Python connector SDK.
Customer-verified connectors and a standard Banner pattern for higher education extend your reach. Reconciliation of out-of-band access changes is built in.
Custom MIM connectors may need equivalent work on Bravura Identity.
Governance that fits how campuses work.
One person can be a student, an employee, and an alumnus at the same time. Bravura Identity brings affiliation modeling and multi-tier role hierarchies built for decentralized institutions.
Advanced separation-of-duties controls are built for FERPA and GLBA access control obligations. Certification and audit trails come with retention controls. Confirm adequacy with your compliance team.
Rule-driven joiner, mover, leaver automation runs across your full environment, on your migration timeline.
Appalachian State University
“We used this moment of temporary chaos to not just fix IAM, but to make the university work better together.”
Matt McNaney, IT Manager, IAM, Appalachian State University
Read how App State modernized IAM →Watch the App State webinar →
Source: Appalachian State University IAM case study, published at bravurasecurity.com
The market pattern
We see the same pattern across the identity governance market.
Cloud-first platforms cover your cloud and Microsoft estate well. Broad coverage of your on-premises and non-Microsoft systems is what sets a platform apart.
MIM transition kit
Two guides. One decision.
Share one with your leadership team and one with your identity team.
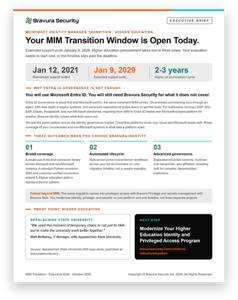
For your leadership team
Executive Brief
Timing, risk, and why Entra ID Governance is not enough on its own.
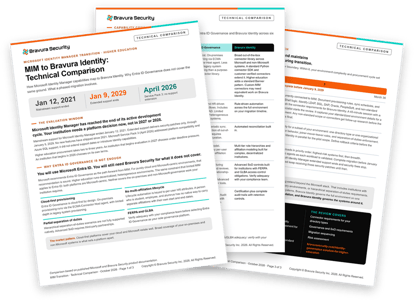
For your identity team
Technical Comparison
MIM, Entra ID Governance, and Bravura Identity side by side, with a phased migration plan.
Download the Technical Comparison
Next step
See what your move off MIM looks like.
Request an architecture review. You start with a 45-minute session with a Bravura Identity specialist. No sales presentation.
We cover your connector requirements, governance and separation-of-duties needs, and migration sequence. Your written fit assessment and phased migration outline follow.